Imagine a pilot receiving what appears to be a legitimate digital message from air traffic control canceling a clearance. The message looks normal. The airplane receives it normally, but the problem is that nobody at air traffic control actually sent it.
The Government Accountability Office says vulnerabilities in aviation communications could allow exactly that kind of spoofing. Its new review found weaknesses involving authentication, encryption, and protocol design in systems pilots and controllers use to exchange text-based information. A malicious actor could potentially transmit fraudulent messages, including a fake clearance cancellation.
Before anyone starts eyeing the passenger sitting in 22B with a laptop, the GAO didn’t say hackers are routinely taking over aircraft communications. It documented vulnerabilities and weaknesses in the government’s ability to detect and respond to attacks. There’s no finding here that a spoofed message has caused an aviation accident.
What the GAO did find should still get your attention.
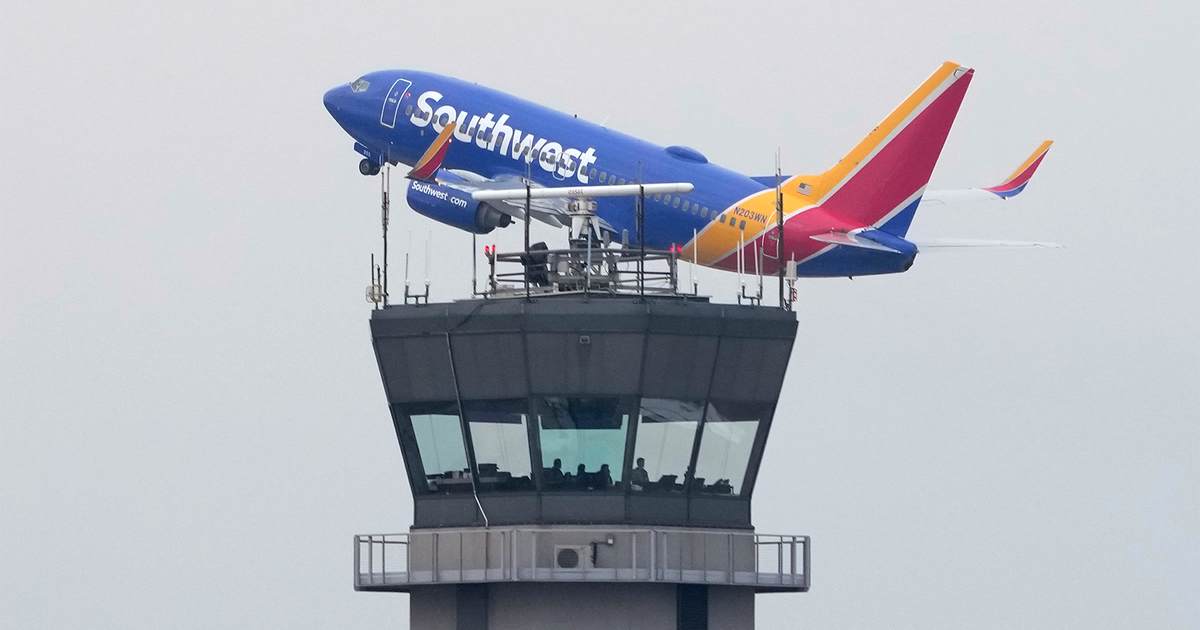
The FAA provides air traffic services for more than 44,000 flights carrying roughly 3 million people every day. Its systems depend heavily on radio frequencies vulnerable to electromagnetic interference, including spoofing and jamming. The FAA knows these threats exist.
The government watchdog examined eight spectrum-dependent systems. For seven of them, the FAA hadn’t completed the formal risk assessments the GAO said were needed to analyze threats such as spoofing and jamming.
Then comes the part I find harder to shrug off.
The GAO says the FAA doesn’t have a defined capability to continuously monitor all of these spectrum threats in real time. Tools capable of detecting such interference exist, but the FAA doesn’t currently have comprehensive coverage. As a result, some incidents can be investigated only after someone reports them.
Recommended: Beijing Added Two More Fentanyl Precursors. The Real Test Starts After Xi Leaves.
In other words, the FAA knows somebody might throw a rock through the window, but in some cases the alarm starts with somebody noticing the broken glass.
The GAO also examined ACARS and CPDLC, communications applications that allow air craft controllers, airlines, and other aviation participants to exchange information digitally. Weak authentication and data protection could allow unauthorized transmissions, spoofed messages, interception, or message tampering.
The possible consequences range from delays and increased workloads for pilots and controllers to degraded situational awareness and, in the worst circumstances, aviation safety problems. None of that requires somebody to “hack the airplane” in the Hollywood sense. Feeding trusted systems false information can create plenty of trouble on its own.
The GAO made nine recommendations. One specifically tells the FAA to develop continuous monitoring for interference, spoofing, and jamming. Another calls for stronger authentication and data protection for ACARS and CPDLC. The Department of Transportation, responding for the FAA, agreed with all nine.
The FAA deserves credit for recognizing the threat, and agreement with the recommendations is a good start. But recognition isn’t detection, and a recommendation isn’t a working system.
More than 44,000 flights will move through American airspace tomorrow. Then another 44,000 or so the day after that.
If someone starts lying to the systems helping guide them, the FAA shouldn’t have to wait for someone else to notice.
PJ Media VIP goes past the headline and into the government reports that deserve more attention. Join today for 60% off with promo code FIGHT.